Attribute AWS integration
Install with Attribute Terraform
To ensure a smooth implementation, Attribute provides a Terraform module that automates setup for billing-information extraction and sensor registration. Detailed Terraform documentation and examples can be found in the [README] within the Terraform module.
AWS Account Types
The module supports installation on both AWS organizational management accounts and member accounts (also known as sub-accounts). Terraform creates all the required infrastructure for the Attribute solution via CloudFormation.
Please note the following:
- Supported Terraform version is 1.9 and above.
- Whenever the sensor needs to be deployed, the Terraform module must be deployed on each sub-account. Additionally, if using a billing or payer account, the module must be deployed on both the billing/payer account and its associated sub-accounts to ensure full cost visibility. We recommend keeping the account installations in the same Terraform state so they're managed together.
- The module does not deploy the Attribute sensor on the compute infrastructure. That process is done with different tools per compute cluster (see Attribute's installation guide).
- The Terraform module must run on
us-east-1, even if the account's resources are in a different region. - When running the module, specify whether you are deploying to the AWS Organization management account or to a member (sub) account where a sensor will be installed, using the
account_typeparameter.
Resources Created by This Module
When running on an AWS management account, the following resources are created:
- S3 bucket and ACLs used to store CUR 2.0 reports and billing data export resources.
- IAM role to allow Attribute to access AWS APIs.
- Data Export resource to facilitate data retrieval.
- CloudFormation stack to automate Attribute Sensor registration.
- EKS (and ECS where applicable) cost allocation tags to support cost tracking.
When running on an AWS member account, the following resources are created:
- IAM role to allow Attribute to access AWS APIs.
- CloudFormation stack to automate Attribute Sensor registration.
Upgrading an Existing Attribute Terraform Module
When upgrading, manually remove the old ZouzCURExport resource.
Appendix A: Detailed Installation Instructions
This appendix walks you through the entire setup process, from the management account configuration to sensor deployment on a member account.
Step 1 — Billing Integration
The following steps should be done only on the management (payer) account.
-
Verify your Terraform version is 1.9 or above:
terraform version -
Make sure you're operating in the
us-east-1region before deploying. -
Update the following variables in the
main.tffile you received from Attribute:- Update the Terraform profile you're using so it points to the correct AWS account.
- Verify the region is set to
us-east-1(do not change to another region). - Verify the alias is set to
"management". - Update the account name from
"change-me"to your account name. - Do not change the
organization_id— leave it as is.
terraform {required_providers {aws = {source = "hashicorp/aws"version = "~> 5.0"}}}provider "aws" {region = "us-east-1"alias = "management"}# provider "aws" {# region = "us-east-1"# alias = "sub-1"# }resource "random_uuid" "external_id" {}module "attribute-sensor" {source = "ZouzIO/attribute-sensor/aws"version = "~> 2.1"account_type = "management"account_name = "change-me"organization_id = "XXXX-XXXX-XXX-XXXX-XXXXXXX"external_id = random_uuid.external_id.idproviders = {aws = aws.management}}# module "attribute-sensor-sub" {# source = "ZouzIO/attribute-sensor/aws"# version = "~> 2.1"## account_type = "sub"# account_name = "change-me-sub"# organization_id = "XXXX-XXXX-XXX-XXXX-XXXXXXX"# external_id = random_uuid.external_id.id## providers = {# aws = aws.sub-1# }# } -
Apply the Terraform:
terraform initterraform apply -
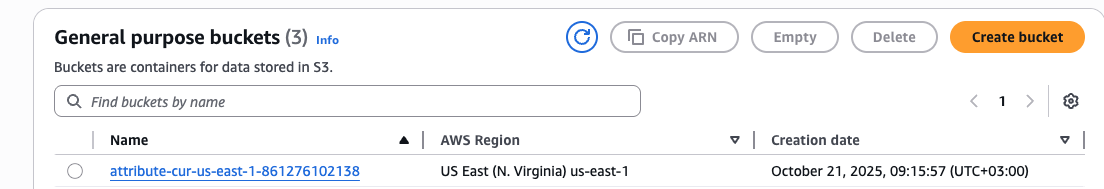
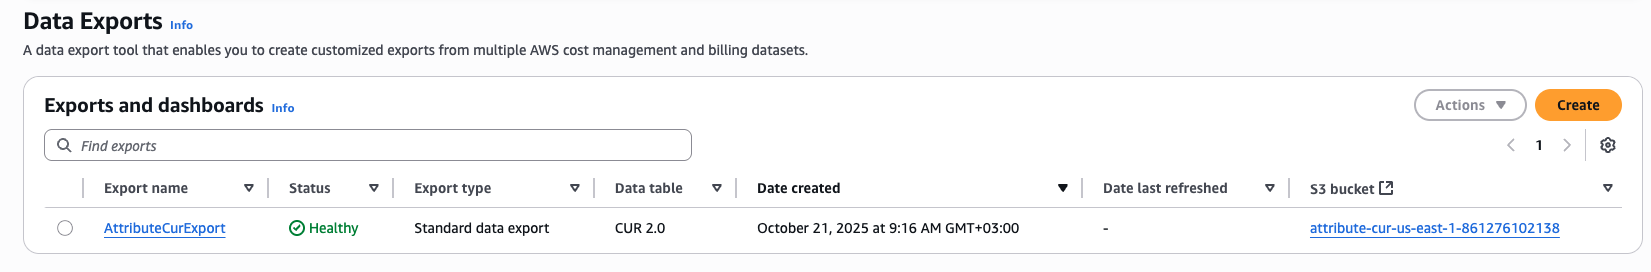
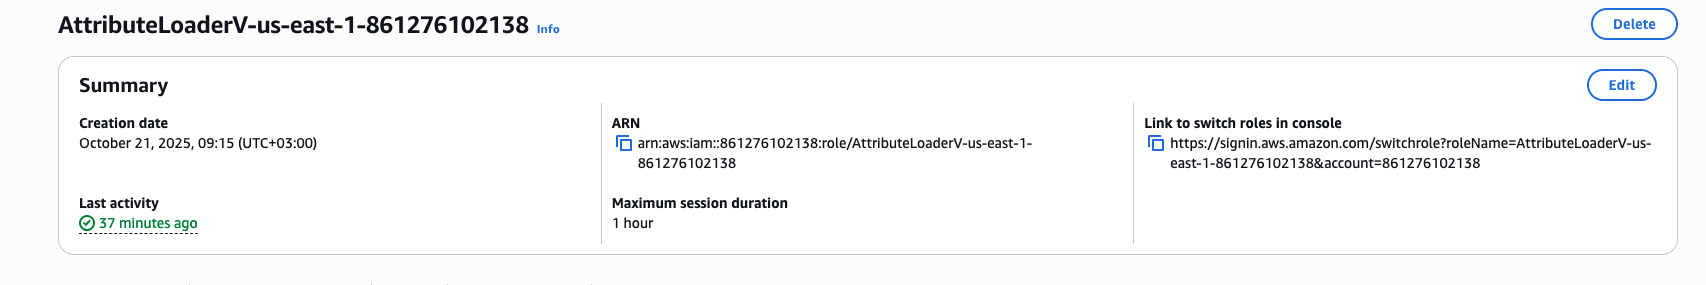
Verification. Log in to your management account's AWS Console and verify that the following resources have been created:
-
An S3 bucket to store CUR 2.0 reports, plus the Data Export.
-
An IAM role that allows Attribute to access AWS APIs.
-
Step 2 — Sensor Implementation
Configure each member account (sub-account) where you plan to deploy a sensor. This involves two parts: running Terraform to create the prerequisites (once per sub-account), and then deploying the sensor on each EKS cluster using a Helm chart.
Step 2.1 — Terraform Prerequisite Setup (Member Account)
The following steps should be run once per member account (sub-account).
-
Update the
main.tffile you received from Attribute to reflect the member account:- Update the Terraform profile to point to the correct AWS account.
- Uncomment the additional provider with the alias of the sub-account (you can have several sub-account providers as needed).
- Uncomment the sub-account module and update the account name from
"change-me-sub"to your sub-account name. - Do not change the
organization_id— leave it as is.
terraform {required_providers {aws = {source = "hashicorp/aws"version = "~> 5.0"}}}provider "aws" {region = "us-east-1"alias = "management"}provider "aws" {region = "us-east-1"alias = "sub-1"}resource "random_uuid" "external_id" {}module "attribute-sensor" {source = "ZouzIO/attribute-sensor/aws"version = "~> 2.1"account_type = "management"account_name = "change-me"organization_id = "XXXX-XXXX-XXX-XXXX-XXXXXXX"external_id = random_uuid.external_id.idproviders = {aws = aws.management}}module "attribute-sensor-sub" {source = "ZouzIO/attribute-sensor/aws"version = "~> 2.1"account_type = "sub"account_name = "change-me-sub"organization_id = "XXXX-XXXX-XXX-XXXX-XXXXXXX"external_id = random_uuid.external_id.idproviders = {aws = aws.sub-1}} -
Apply the Terraform:
terraform apply -
Verification. Log in to your sub-account on the AWS Console and verify that an IAM role allowing Attribute to access AWS APIs has been created.
Step 2.2 — Deploying the Sensor with Helm on EKS
The following steps should be repeated on every EKS cluster where you want to deploy the sensor.
-
Save the values file provided by Attribute (
values.yaml). This file contains a unique ephemeral token. -
Review the Java instrumentation settings in the values file. The file includes the following flags by default:
# Java instrumentation settingssensorDisableAutoJavaInstrumentation: truejavaAutoInject:enabled: trueThis configuration is supported on Kubernetes 1.28 and above. The injection backend is selected automatically, so no version-specific adjustment is needed.
To use the sensor's dynamic Java instrumentation instead of admission-time injection, set
javaAutoInject.enabledtofalseand setsensorDisableAutoJavaInstrumentationtofalse. The two must never be enabled together. For a full explanation of both modes, see the Attribute Java Instrumentation Guide. -
Verify your Helm version — version 3.8.0 or above is supported:
helm version -
Install the Helm chart:
helm upgrade -i attribute \oci://quay.io/attribute/operator-chart \-f <values.yaml> \-n attribute \--create-namespace -
Optional — configure the token as a secret. If you'd like to store the token as a secret using an external secret manager, add the following configuration to the values file:
initconfig:create_secret: falseorgToken:secretName: external-secret-namesecretKey: external-secret-key -
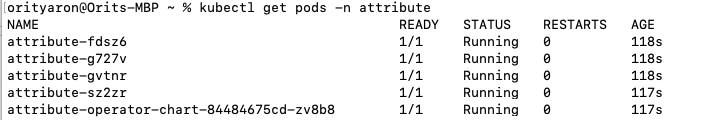
Verification. Run the following to verify the Helm release and that the operator and sensor are running:
helm list -n attributekubectl get pods -n attributeExample expected output:

If you'd like to deploy the sensor on other compute resource types (standalone, Fargate, etc.), refer to the relevant sensor deployment documentation.
Trademarks: AWS is a trademark of Amazon.com, Inc. or its affiliates. Terraform is a registered trademark of HashiCorp, Inc. Kubernetes is a registered trademark of The Linux Foundation. All other trademarks are the property of their respective owners.